Reference · Foundation
Payment fraud includes stolen access and manipulated consent
A transaction can be technically authorized by the real account holder and still be the result of a scam.
Payments & Account FraudReviewed Aug 15, 2026
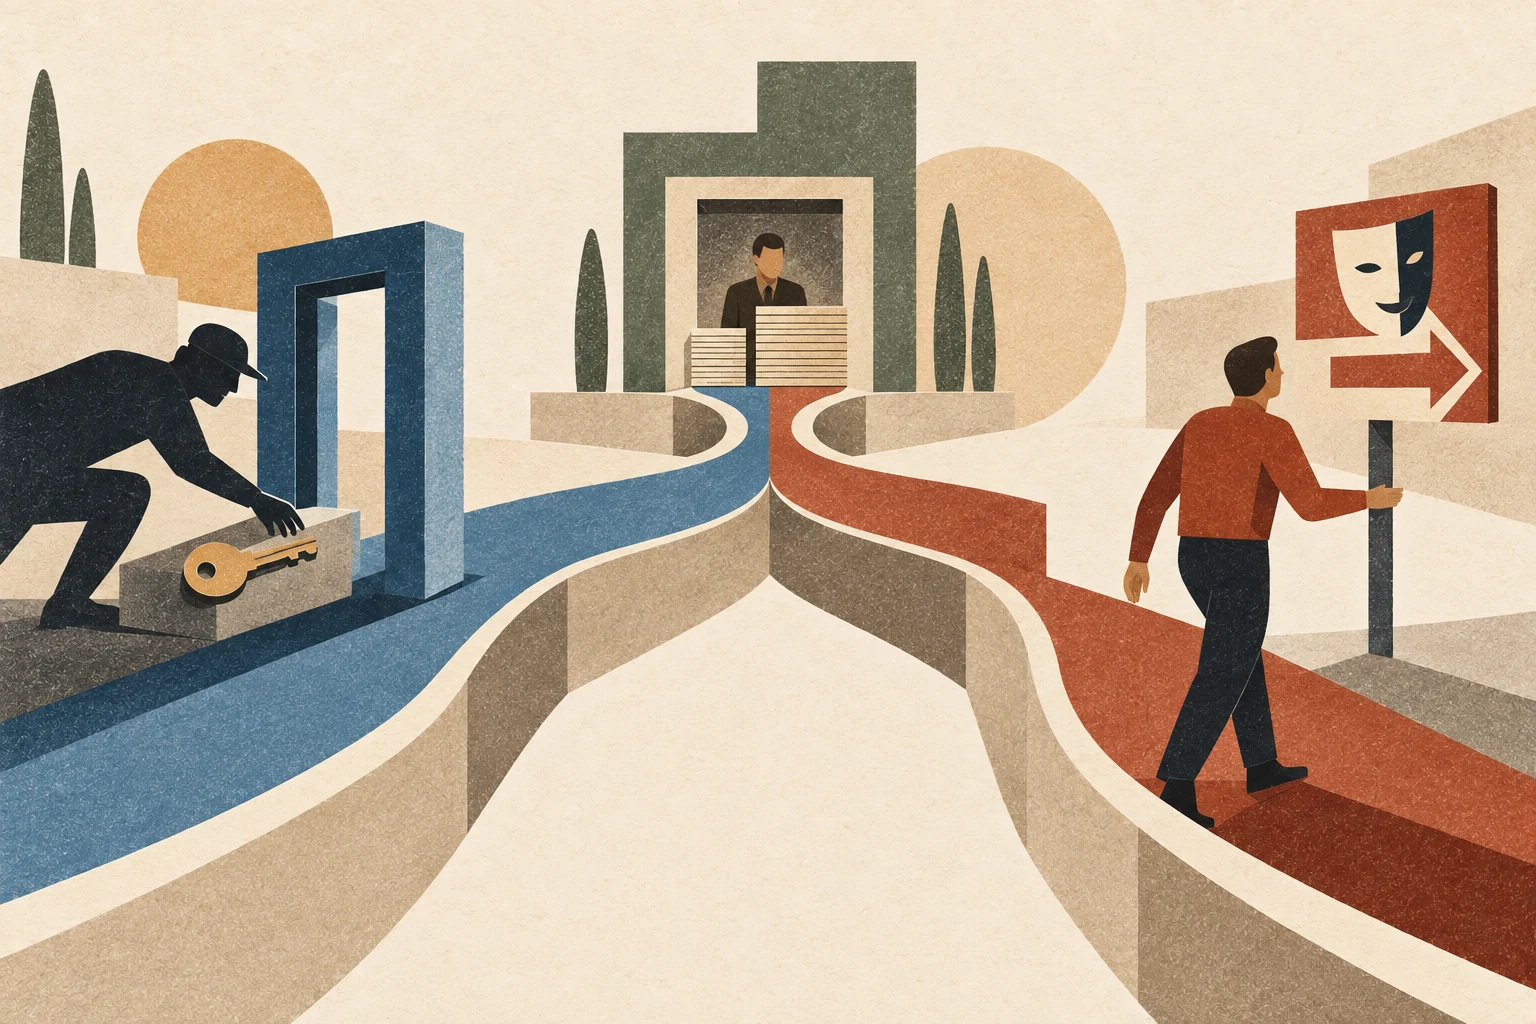
Two broad paths
Unauthorized payment fraud occurs when someone uses an account, card, credential, or payment instrument without valid permission. In an authorized-payment scam, the real customer initiates or approves the transfer because an attacker has deceived them about the recipient or reason.
Why controls differ
Credential and device signals may help with stolen-account activity. They can be less decisive when the legitimate customer is using a familiar device and passes authentication. Then the payee, payment purpose, urgency, communication pattern, prior behavior, and customer warning experience may matter more.
Do not flatten the taxonomy
Card fraud, ACH fraud, wire fraud, refund abuse, merchant fraud, first-party misuse, and authorized-push-payment scams have different evidence and rules. A useful investigation identifies the payment rail, who controlled the account, who benefited, what representation was made, and which decision point could have interrupted the loss.
Add friction where consequence is highest
A new payee, unusual destination or high-consequence account change may justify an extra confirmation or a short review. Friction should be targeted and measured because blanket delay can harm legitimate users without stopping adaptive attackers. A control needs an owner, a reason code and outcome feedback; a warning screen alone is not proof that the risk was understood.
Example: the account holder sends the transfer
A scammer posing as a bank persuades a customer to move money into a “safe” account. The customer authenticated and submitted the payment, but consent was manipulated. The bank’s account-access evidence and the customer’s scam report describe different parts of the event. A useful review examines the communication, destination, timing and warnings without reducing the case to a single authentication result.
Controls need a clear customer path
A warning or review can help only when the customer understands what is unusual and can reach legitimate support safely. Design escalation, reversal and complaint routes before the event, and measure how often controls stop harm versus delay ordinary payments. Applicable rights and liability depend on payment type and law; a general guide cannot decide a specific claim.
Related reading
Keep exploring the subject
Related guide
Rules, risk scores, explainability
A score can combine evidence, but investigators and control owners still need to know what moved it and what action follows.
Related guide
Cybersecurity and fraud
A stolen login can begin as a cyber incident and end as fraud. Other scams need no software exploit at all.
Explore
Browse all Security & Fraud topics
Choose another subject or question.