Security & FraudPublished by Svertok:
Ask software vendors who owns the security work after the sale
The strongest security answer names an owner, update period, disclosure path and recovery plan after the sale.
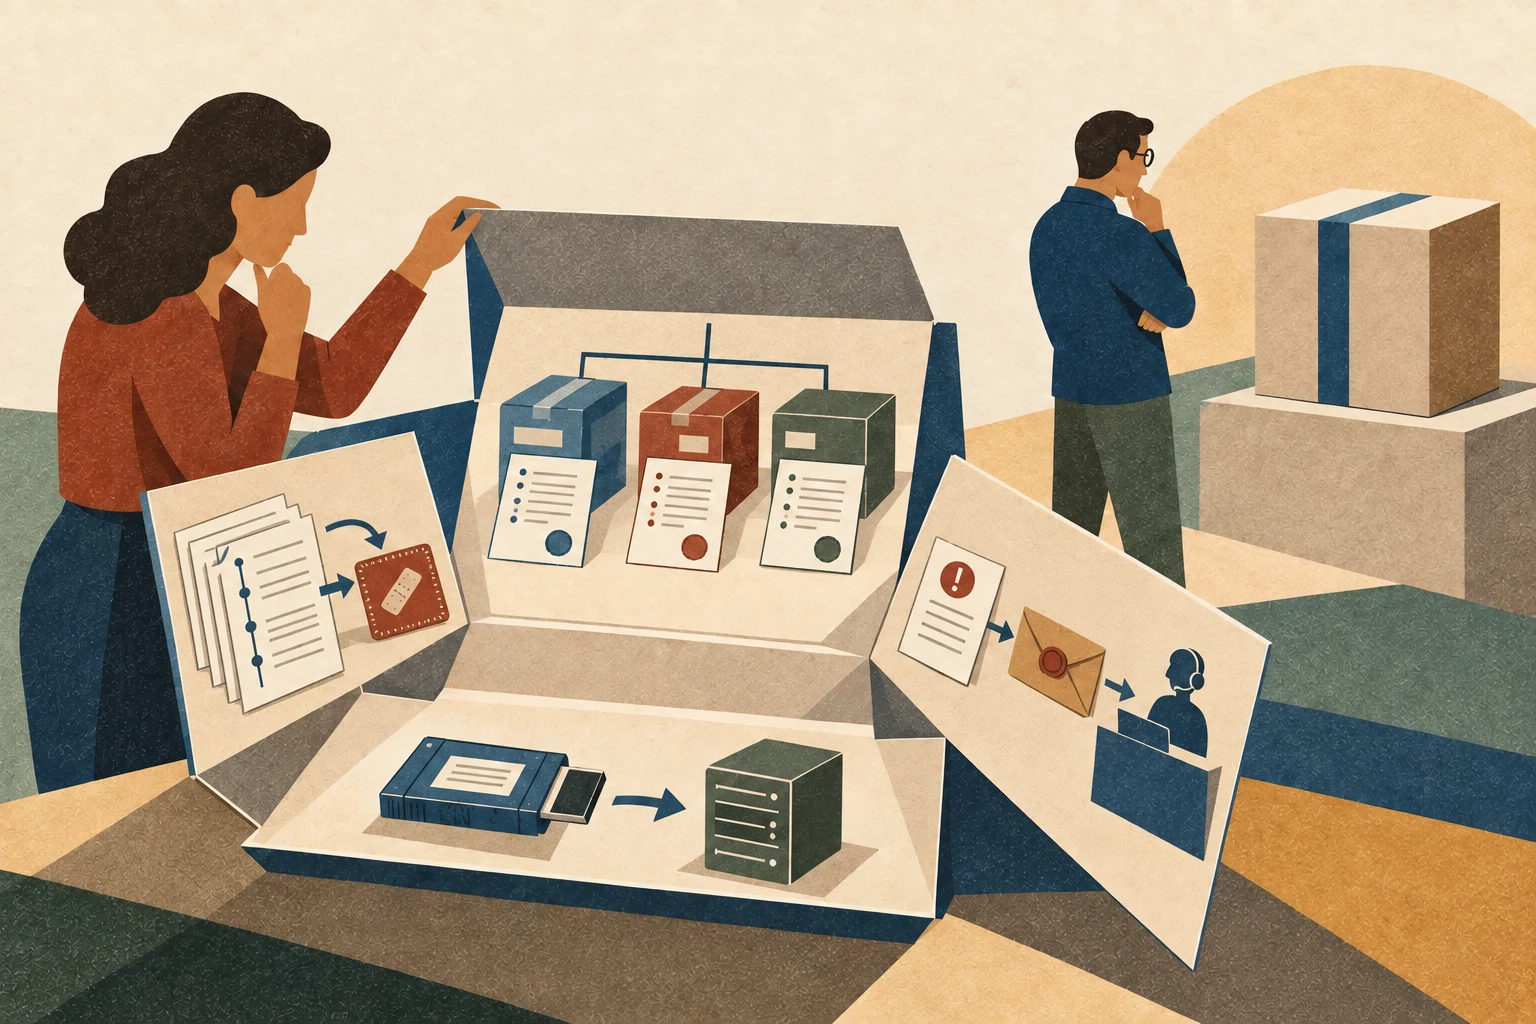
Who owns security after launch?
Ask who receives vulnerability reports, how researchers can contact the company and how customers hear about material issues. A precise answer names a process and an accountable team. “We take security seriously” says nothing about what happens when a flaw is found on a Friday night.
How long will this version be fixed?
Get the supported versions, update channel and end-of-support policy in writing. Ask whether critical fixes can arrive without a paid upgrade and how quickly customers are expected to install them. If the product depends on a cloud service, include service shutdown, data export and account deletion in the same conversation.
Can the company prove recovery?
Authentication, access review, backup and incident response should cover the product’s real architecture. Ask which logs are available, how tenant data is separated and what customers must configure themselves. No questionnaire guarantees secure software. Good answers do reveal whether the supplier has designed an operating lifecycle or only a polished sales demo.
Ask for evidence that survives the sales meeting
Useful answers arrive as support policies, security documentation, contract terms, sample notifications or a clear shared-responsibility statement. Save the version that informed the purchase and note who owns each obligation. A promise made only in conversation is hard to operate when the product changes or an incident occurs. The aim is not to demand a perfect vendor. It is to know which security work the supplier performs, which work remains with the customer and how both sides will recognize a material failure.
Next
CISA flags a Citrix NetScaler memory-buffer flaw as actively exploited
CVE-2026-88779 has entered the Known Exploited Vulnerabilities catalog, raising its remediation priority while leaving the attackers and campaign scale unidentified.
Read next
GitLab urges immediate updates for critical self-hosted AI Gateway flaw
A crafted flow configuration could let an authenticated Duo Agent Platform user escape a prompt-template sandbox and execute commands on the gateway. GitLab rates the issue CVSS 9.9.
Read
CISA Flags a FortiMail Path-Traversal Flaw as Actively Exploited
CVE-2026-104286 is now in the federal exploited-vulnerability catalog, raising its remediation priority while the short alert does not provide affected versions or attack details.
Read