Explainer · Practitioner
Software supply-chain risk enters through something you chose to trust
A dependency, update path, build system, or vendor can carry risk into many downstream environments at once.
Web / Application / API SecurityReviewed Aug 15, 2026
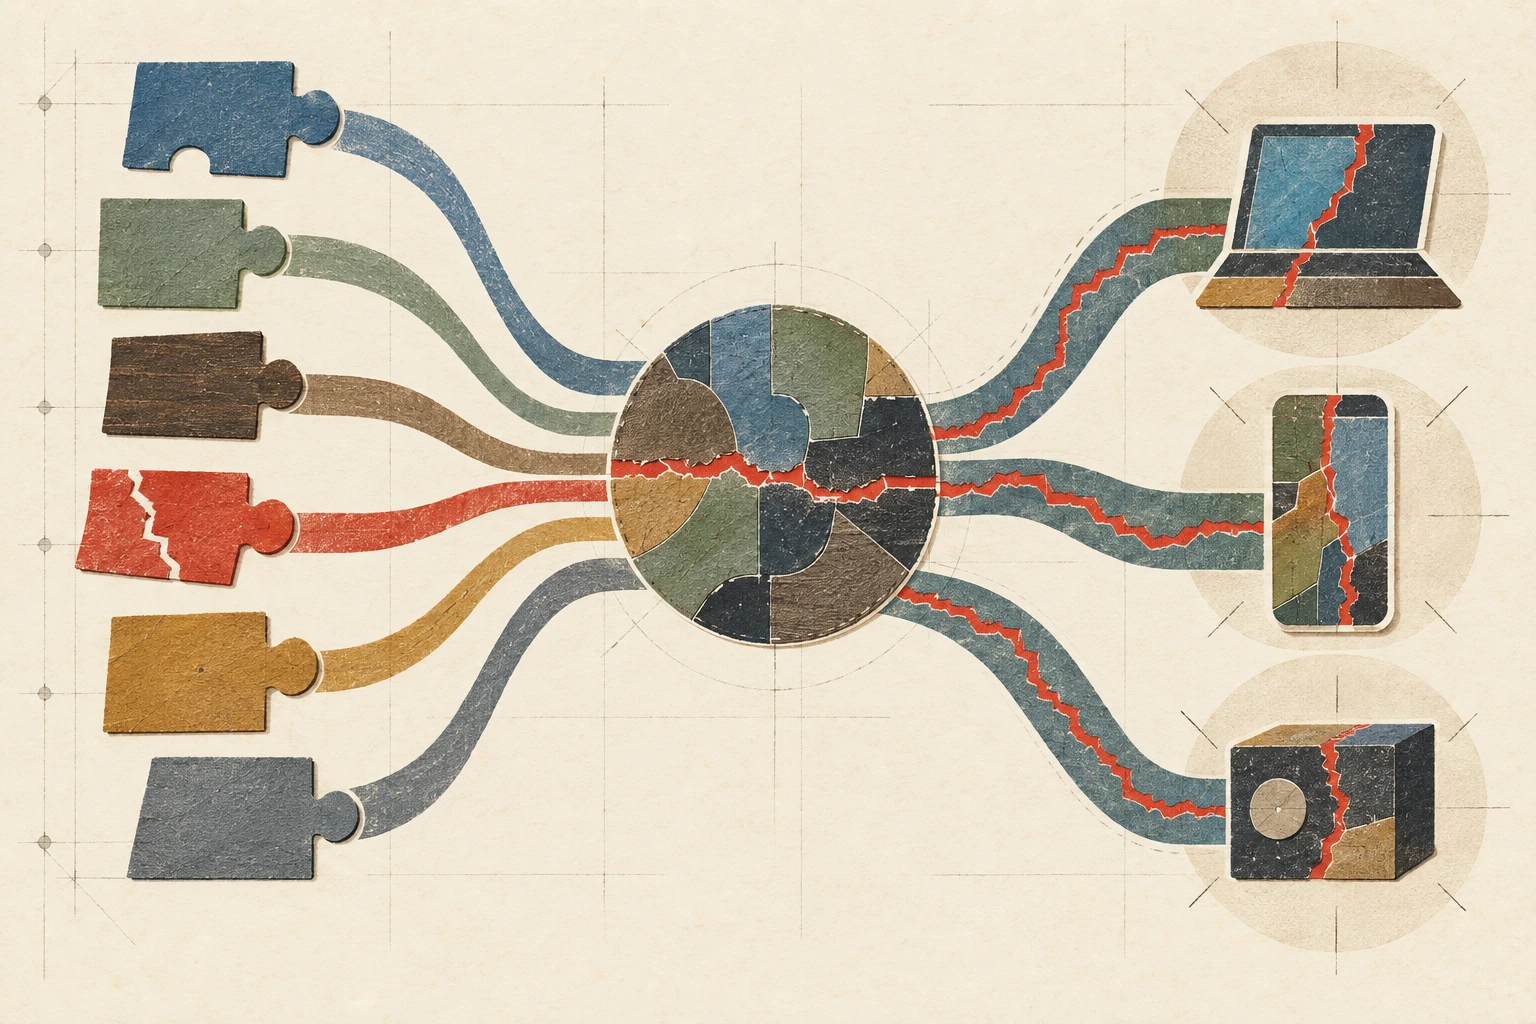
The trusted path
Modern software depends on libraries, package registries, build services, signing systems, vendors, and update channels. A compromise or integrity failure in one of those paths can be distributed through software that customers intentionally install or run.
Different failures need different responses
A vulnerable open-source library, a malicious package, a stolen signing key, a compromised build pipeline, and a breached service provider are related supply-chain concerns but not the same event. The affected component, delivery path, versions, privileges, and downstream reach determine the response.
Reduce surprise
Maintain a useful dependency and vendor inventory, verify update provenance, restrict build and release privileges, monitor high-impact changes, plan for component replacement, and require vendors to communicate material incidents. An inventory helps only if owners can map a notice to deployed systems and act.
A dependency needs an owner and version
The same library can appear directly, arrive through another package or be embedded in a vendor product. Record which build uses it, who owns the product and how the supplier communicates changes. A component name without the deployed version and product relationship is difficult to turn into a safe update decision.
Provenance supports but does not replace review
Signed artifacts, controlled builds and an SBOM can help establish where software came from and what it contains. They do not prove that the code is free of flaws or that the deployed configuration is safe. Teams still need vulnerability response, supplier communication, testing and a rollback path that reaches the actual product in service.
Example: the flaw is fixed upstream but not deployed downstream
A library maintainer releases a patch, yet a commercial product that embeds the library has not shipped an updated build. The component fix exists, but the customer cannot safely substitute it without vendor support. Inventory should connect component, supplier product, deployed version and owner so the team can track the downstream remedy rather than closing the issue at the upstream announcement.
Supplier questions that lead to action
Ask how the supplier identifies dependencies, signs and distributes updates, communicates a material flaw and supports rollback. Request the scope and cadence of an SBOM where appropriate, but do not treat the document as a safety certificate. Contract language and attestations matter only when an owner can use them during a real change or incident.
Related reading
Keep exploring the subject
Related guide
Incident response
Preparation, detection, containment, recovery, communication, and learning belong to one risk-management loop.
Related guide
Application and API security
Broken access control, injection, unsafe design, and weak logging are different failures with one common lesson: every request needs context.
Explore
Browse all Security & Fraud topics
Choose another subject or question.